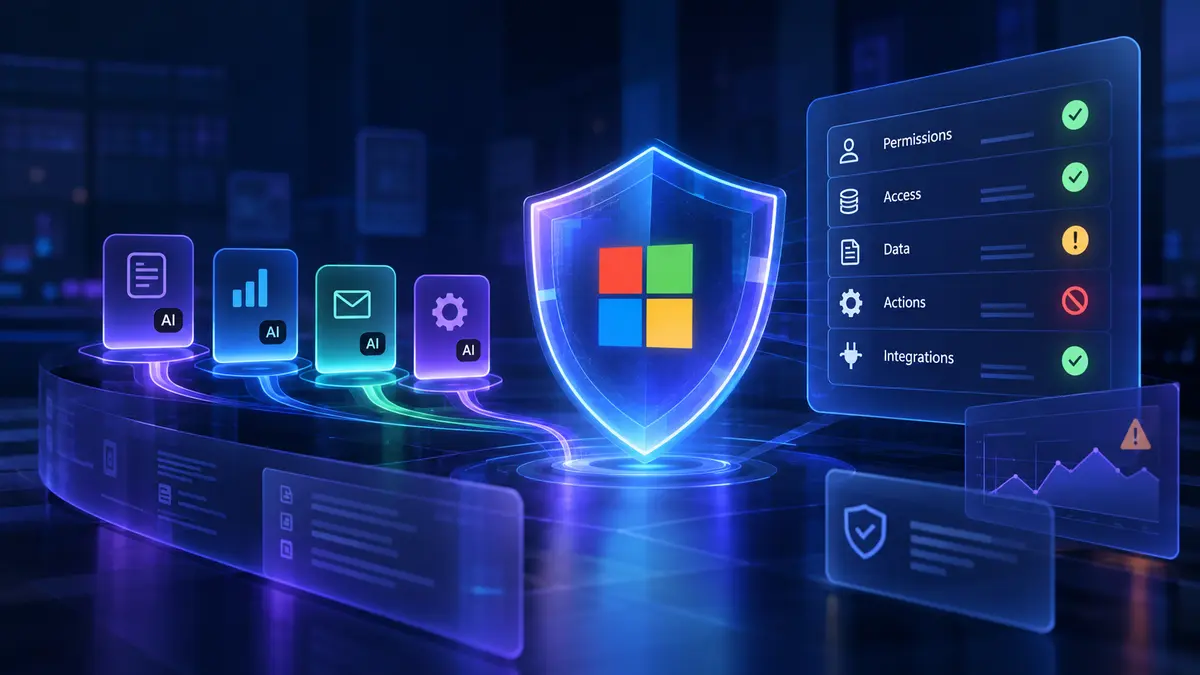
An agent can start with a harmless job and end up with access it never needed. A customer-support assistant that reads tickets may also have permission to issue refunds, email a customer list or delete records because all those operations sit behind the same integration.
What actually happened
On October 19, Microsoft described an expansion of Project Perception aimed at securing autonomous agents operating inside organizations. Its Guardian Agents are designed to observe activity, investigate changing risk and recommend or apply containment through policies and playbooks set by people.
Microsoft's framing is that agents should be treated as potentially unreliable insiders, even when their owners deployed them legitimately. The company links this approach to agent discovery, identity, changing permissions and access controls across enterprise systems. These are Microsoft product capabilities and architectural claims, not evidence that all organizations need this particular product.
Why a small team cares
Take a small marketing agency using an AI agent to maintain a client's CRM. It reads new leads, enriches records and prepares follow-up messages. That is useful work, but the same integration might have permission to export the whole contact database or send messages without review.
If the agent mistakes a note for an instruction, or encounters hostile text in an imported record, the issue is no longer answer quality. It is whether the system has granted the agent authority to perform an unwanted action. Small teams may not have a dedicated security department, so the design of the workflow has to carry more of the safety burden.
An explicit owner, narrow credentials and audit logs make it possible to trace what the automation did. Separating routine data preparation from customer-facing or financial actions lets the team keep most of the time saving without accepting every risk of full autonomy.
Hype vs useful
Guardian Agents sound like the start of an entirely new security market. For a five-person business, though, the first useful step is usually simpler than deploying a second agent to supervise the first.
The key idea is that permission checks must live outside the language model. Asking an agent to 'be careful' is not access control. A workflow platform, API permission or approval mechanism should decide which operations are allowed, and a person should retain control where mistakes have a meaningful business cost.
Microsoft is building for organizations with large agent fleets. Small teams should watch where these controls become accessible through tools they already pay for. Until then, disciplined permissions and clear approval boundaries solve more immediate problems than another security dashboard.