A clean dependency audit can still miss a vulnerability in the runtime underneath an application. That distinction matters for teams deploying Node.js services through containers, PaaS platforms and automated build pipelines.
What actually happened
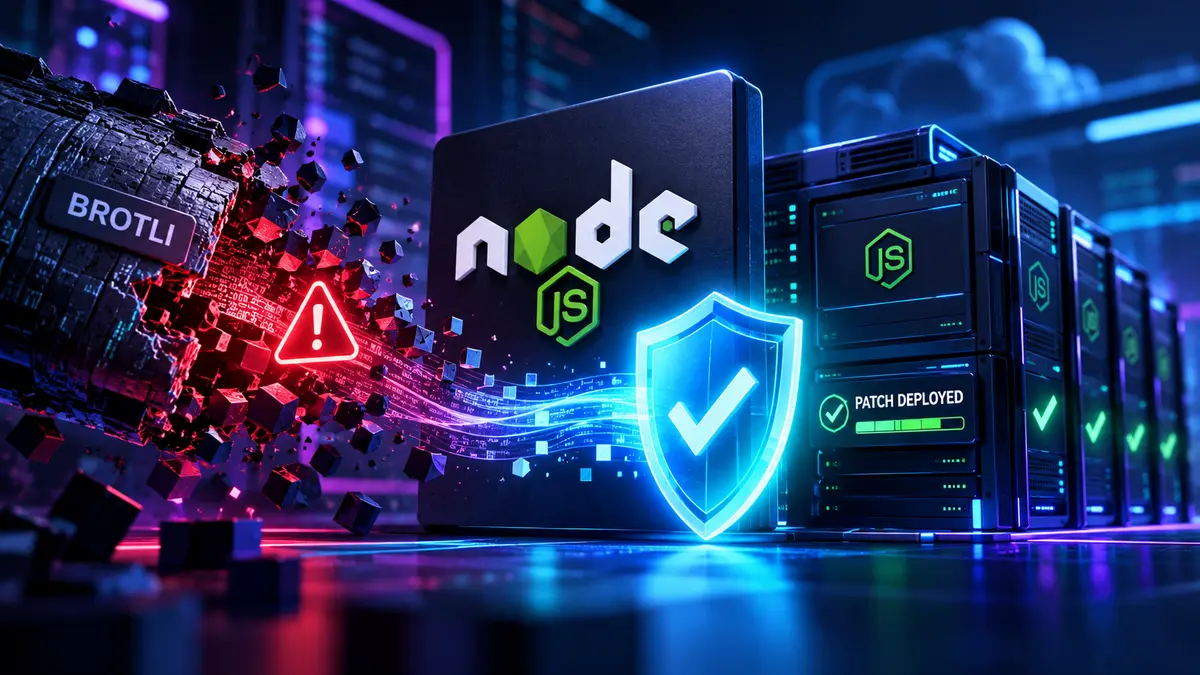
The Node.js project issued security releases on October 21 for its supported 22.x, 24.x and 26.x lines. One of the high-severity fixes, CVE-2026-111497, addresses a buffer overrun in the bundled Brotli decompressor. Malformed compressed input can lead to process crashes, memory disclosure or remote code execution when an application decodes attacker-controlled Brotli data through node:zlib.
The minimum patched versions are 22.23.4, 24.22.1 and 26.12.1 respectively. The same release round addresses several other DNS, TLS, crypto and permission issues. Node.js explicitly excludes end-of-life lines from its supported security releases, so older installations need an upgrade path rather than a promise that an npm package will fix the problem.
Why a small team cares
Consider a small software company whose customer-facing API is deployed in a Docker image. The source repository may show current package versions while the production image still contains an earlier Node binary. A successful CI build does not prove the runtime in a running instance changed, particularly if an old base image or cached layer survives.
The risk is clearest where compressed data comes from external sources, such as an upload-processing service or proxy integration. Exploitability depends on the application's input path and decoding behavior, so every Node deployment is not automatically an exposed remote-code-execution endpoint. But the remediation is a runtime patch, and leaving supported production installations behind creates avoidable exposure.
Hype vs useful
The word 'critical' is circulating in coverage, but the Node.js project rates this particular issue High. Remote code execution is a possible outcome, not a confirmed compromise of every affected service. That distinction should guide prioritization without becoming an excuse for delay.
A useful verification is the Node version reported inside the actual running image or host, plus a check that traffic and jobs behave normally after the rollout. A package-lock change or a green security scanner against application dependencies is not enough evidence.