A website can show a perfectly respectable consent banner and still fail the moment a visitor changes their mind. The banner updates, the interface confirms the new preference, but an analytics or advertising script keeps reading information already stored in the browser. For a small site owner, that gap is easy to miss because nothing visibly breaks.
What actually happened
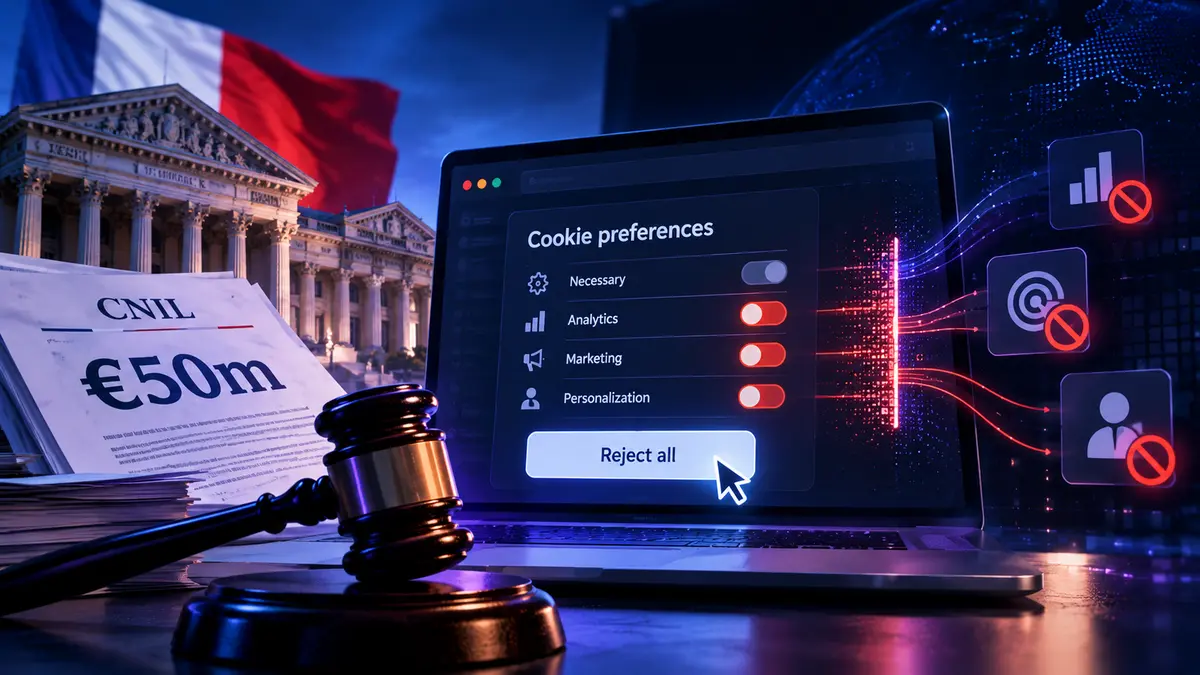
On October 16, 2026, France's Conseil d'État rejected Orange's challenge to a €50 million fine imposed by the CNIL in 2024. The sanction covered two separate practices: advertisements displayed like messages inside the Mail Orange inbox, and access to information stored on users' devices after they had withdrawn their consent.
On the cookie issue, the court confirmed that reading stored information after consent was withdrawn can breach Article 82 of France's Data Protection Act, even when the information is not subsequently processed. The decision also addresses the email-like advertising practice and confirms that CNIL was not obliged to issue a warning before pursuing a penalty.
The fine was a combined sanction involving Orange's particular circumstances. It is not a new standard €50 million penalty for a broken cookie banner. Nor does the ruling prohibit all cookies: access that qualifies for a lawful consent exemption remains a separate category.
Why a small team cares
Imagine a small WordPress store using a consent-management plugin, Google Tag Manager, analytics and two advertising integrations. The owner checks that visitors can reject cookies on first arrival. Everything appears correct, so the site goes live.
Months later, a visitor accepts tracking, then returns to the preference panel and withdraws consent. The plugin records that new preference, but an existing script continues reading an advertising identifier on the next page. Another integration may initialize again because its GTM trigger checks whether consent was ever granted rather than its current state.
That is not something a site owner can reliably judge by looking at the banner. The actual test is operational: consent, withdraw, reload, navigate and inspect what the browser and tags do afterwards. A Shopify merchant can face a similar issue when apps or custom pixels are not aligned with the consent controls.
Hype vs useful
The easy headline is that Orange lost a €50 million case. The useful lesson is narrower and more actionable: withdrawing consent has to change what the site does, not merely which setting is displayed.
A browser network panel, consent debugger and cookie inventory can show whether known tags continue operating. Cookie deletion alone is not a complete test, and a single quiet network request is not conclusive proof of compliance. You need to distinguish consent-dependent storage and access from exempt operations, and test the routes where scripts actually load.
I would prioritize this over another cosmetic banner redesign. For smaller businesses, a short, documented test of withdrawal behavior is more valuable than a polished consent dialog whose underlying integrations nobody has checked.