What actually happened
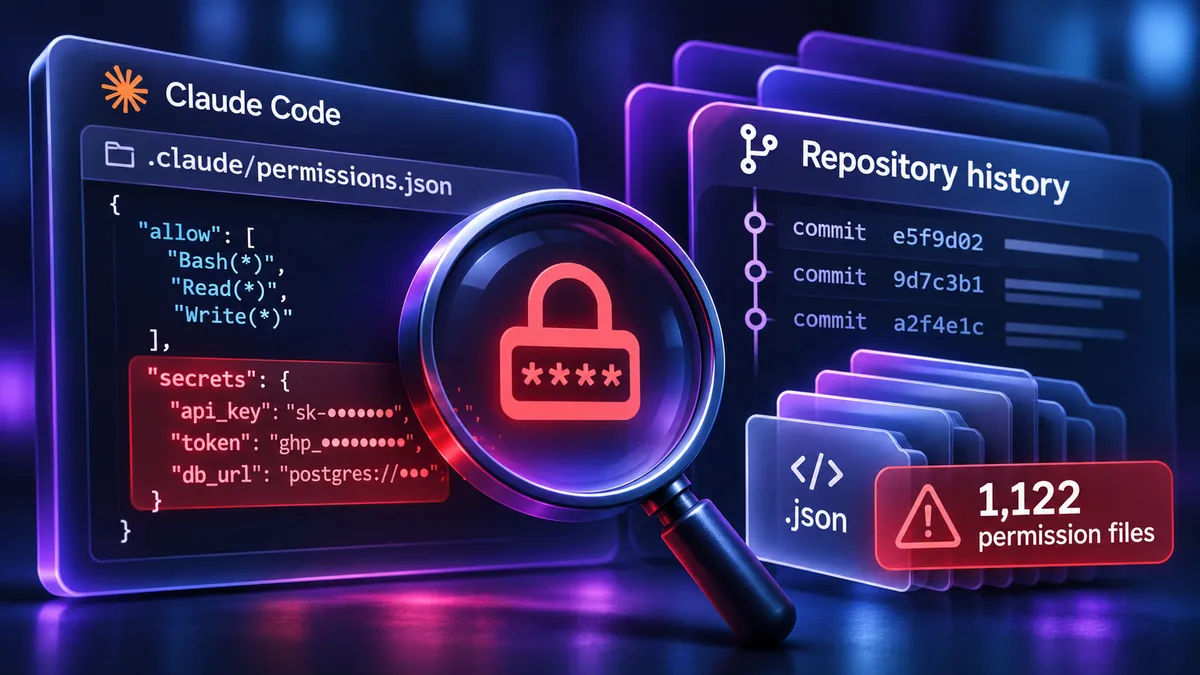
The risky step is an ordinary permission click. When a developer selects "Yes, and don't ask again" for a shell command, Claude Code can save the exact approved command in the project's `.claude/settings.local.json` file. If the command contains an inline password, connection string or API token, the permission rule can preserve that credential in plain text. Claude Code does not automatically publish the file. Exposure happens when a developer or agent subsequently commits it.
In research published on 5 November, security firm Apiiro found 104,185 public copies of that settings file across 103,617 GitHub repositories. It classified 1,379 distinct credentials in 1,122 files. Its larger figure of 2,539 includes additional sources such as previous commits, shared settings and agent transcripts. These are researcher-identified secrets, not 2,539 confirmed working credentials; Apiiro says it did not test them.
Why a small team cares
Picture a six-person web agency debugging a client's staging database. A developer gives Claude Code permission to reuse a database command and later commits the project folder. A production credential may now travel with the repository even if the original `.env` file is safely excluded. The issue is a second copy produced by an approval workflow, not necessarily a failure in the normal secrets manager.
Deleting the current file is not the end of the incident. Earlier commits, forks, clones and exported project files can retain the value, while the password remains usable until its owner revokes it. This is particularly awkward for small teams because permission settings look like harmless developer preferences and can escape the code-review attention given to application source.
Hype vs useful
Claude Code does attempt to protect its local settings file by registering a Git exclusion on the developer's machine. That protection does not reliably follow the repository to a teammate's clone or cover a file already tracked. Apiiro also reported that 215 of the 1,122 affected files were missed by both gitleaks and TruffleHog, underscoring the limits of relying solely on default secret patterns.
Anthropic has acknowledged the issue and is considering mitigations, but a possible future product fix does not invalidate credentials already copied into Git history. The useful lesson goes beyond Claude Code: agent approval records, transcripts and generated notes can become a second credentials surface. Treat them as part of the software delivery process, not as disposable chat history.