A working internal tool can look finished while its access settings expose customer or employee information. Claroc's research is a reason to check who can actually open and use the applications your team has published.
What actually happened
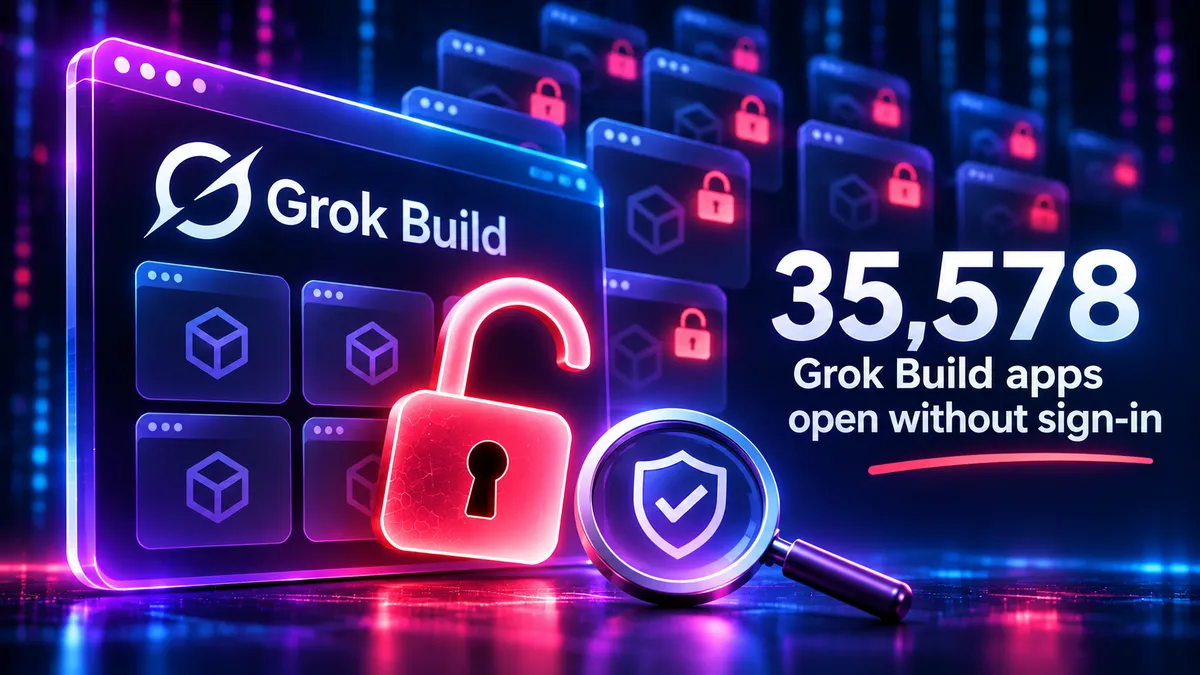
On 10 November, Claroc reported finding 43,601 Grok app addresses and trying 43,551. Of 37,571 that were still online, 35,578 opened without signing in. Most were ordinary apps, but the researchers reported examples containing internal business information, personal data and plaintext passwords in browser-delivered code.
Claroc tested two apps it built itself and found that outsiders could modify their data under the tested settings. It did not test write access on other people's apps. It also reported that 24 open apps built by SpaceXSI and X staff were taken down after disclosure; it did not report the removal of all other open apps.
Why a small team cares
An app address that seems obscure is not a substitute for authentication. Claroc says published app hostnames can appear in passive DNS records, making them discoverable even when the creator has not deliberately shared the link widely.
A simple customer list, staffing tool or prototype may acquire sensitive information as people use it. If sign-in checks identity without checking authorization, an outside account may still gain access. The risk extends beyond one app builder.
Hype vs useful
These are Claroc's observations, not an independent test by 8digits. The company says that in its test account the publishing panel proposed access for anyone with the link; SpaceXSI told a reporter that apps are private until shared and that employee accounts start with Only you. Access settings may differ or change, so verify the current behaviour on your own account.